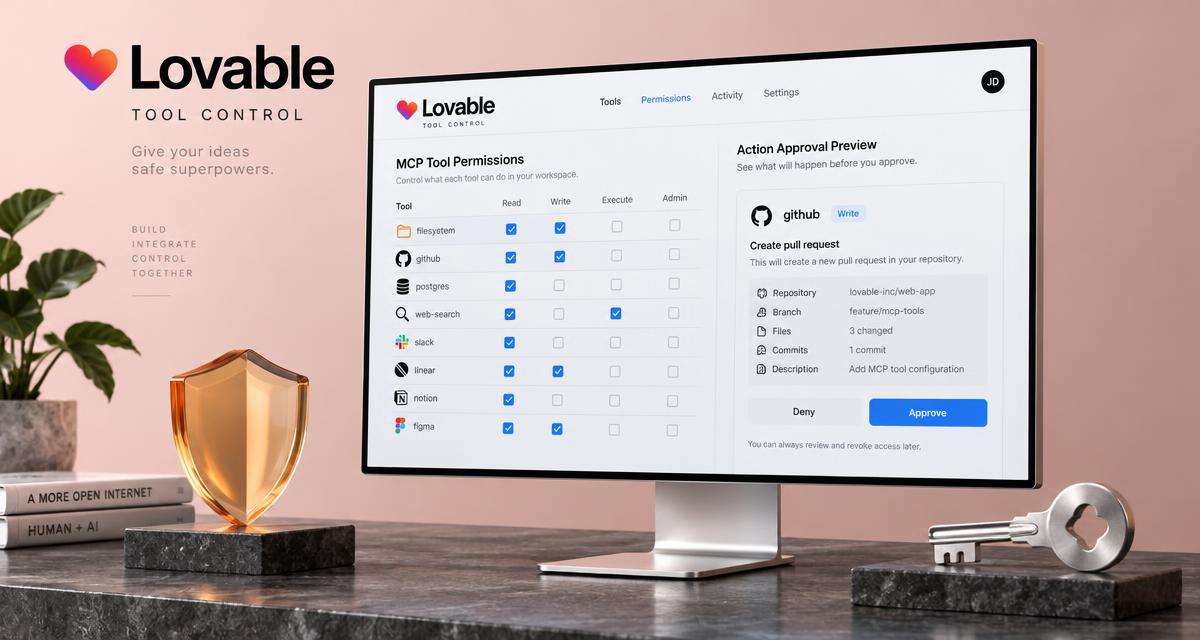
A connected tool is not automatically a trusted tool. Build a permissions catalogue, change review and an approval gate for write actions in Lovable.
MCP standardizes how agents discover and call tools; it does not make every server safe. OWASP documents tool poisoning and changed tool definitions among the risks. This build tracks tool descriptions and allowed actions, pauses on catalogue changes and shows the exact write payload before approval. A dashboard alone is not enforcement: checks must run in the server-side tool path, with user-scoped authorization.
- Per-user connections with protected OAuth material
- Versioned tool catalogue and review records
- Runtime MCP client in server-side agent execution
- Pending actions, immutable approvals and audit events
Offer tool onboarding and permission maintenance to teams already using agents. Do not sell this prototype as a certified audit or a guarantee against prompt injection. Track blocked unapproved changes and review time.
Integration-dependent: test one read tool first
- Choose one documented remote MCP server. Use HTTPS and an allowlist; block private network targets and redirects before connecting.
- Authenticate the app user and complete the server's supported OAuth flow. Never store access tokens in tool descriptions or browser logs.
- Fetch the tool catalogue and store names, schemas, descriptions and a version fingerprint. Classify tools as read, write or privileged.
- Require an owner review before enabling a new tool or changed definition. Treat descriptions and tool results as untrusted content.
- Start with a read-only tool. Enforce user-scoped access on every invocation; the model cannot choose a different user ID.
- For writes, persist the exact tool, arguments, destination and expiry as a pending action. Approval must bind to that immutable payload.
- Recheck identity, permission, expiry and payload hash at execution. Changed arguments, reused approval or a changed tool definition must stop the action.
- Log redacted outcomes, close MCP clients on completion and test revoked access, malicious descriptions, cross-user calls and duplicate approvals.
Build an MCP tool review workspace for an existing runtime AI agent. Use a server-side MCP client with one documented HTTPS server and its supported OAuth flow. Persist connections per authenticated user; protect tokens server-side. Block private-network targets and redirects. Version tool names, schemas and descriptions; disable new or changed tools pending owner review. Enforce access and allowed tools at runtime, never from model-supplied user IDs. Read tools first. Persist exact write payloads with expiry; require single-use approval bound to the immutable payload and revalidate authorization at execution. Treat descriptions and results as untrusted. Redact logs, close clients and test malicious descriptions, revoked tokens, cross-user requests and duplicate approvals. This is not a security certification.